Cybersecurity and Firewalls
Firewall policy, segmentation and endpoint protection designed around how your organisation actually operates.
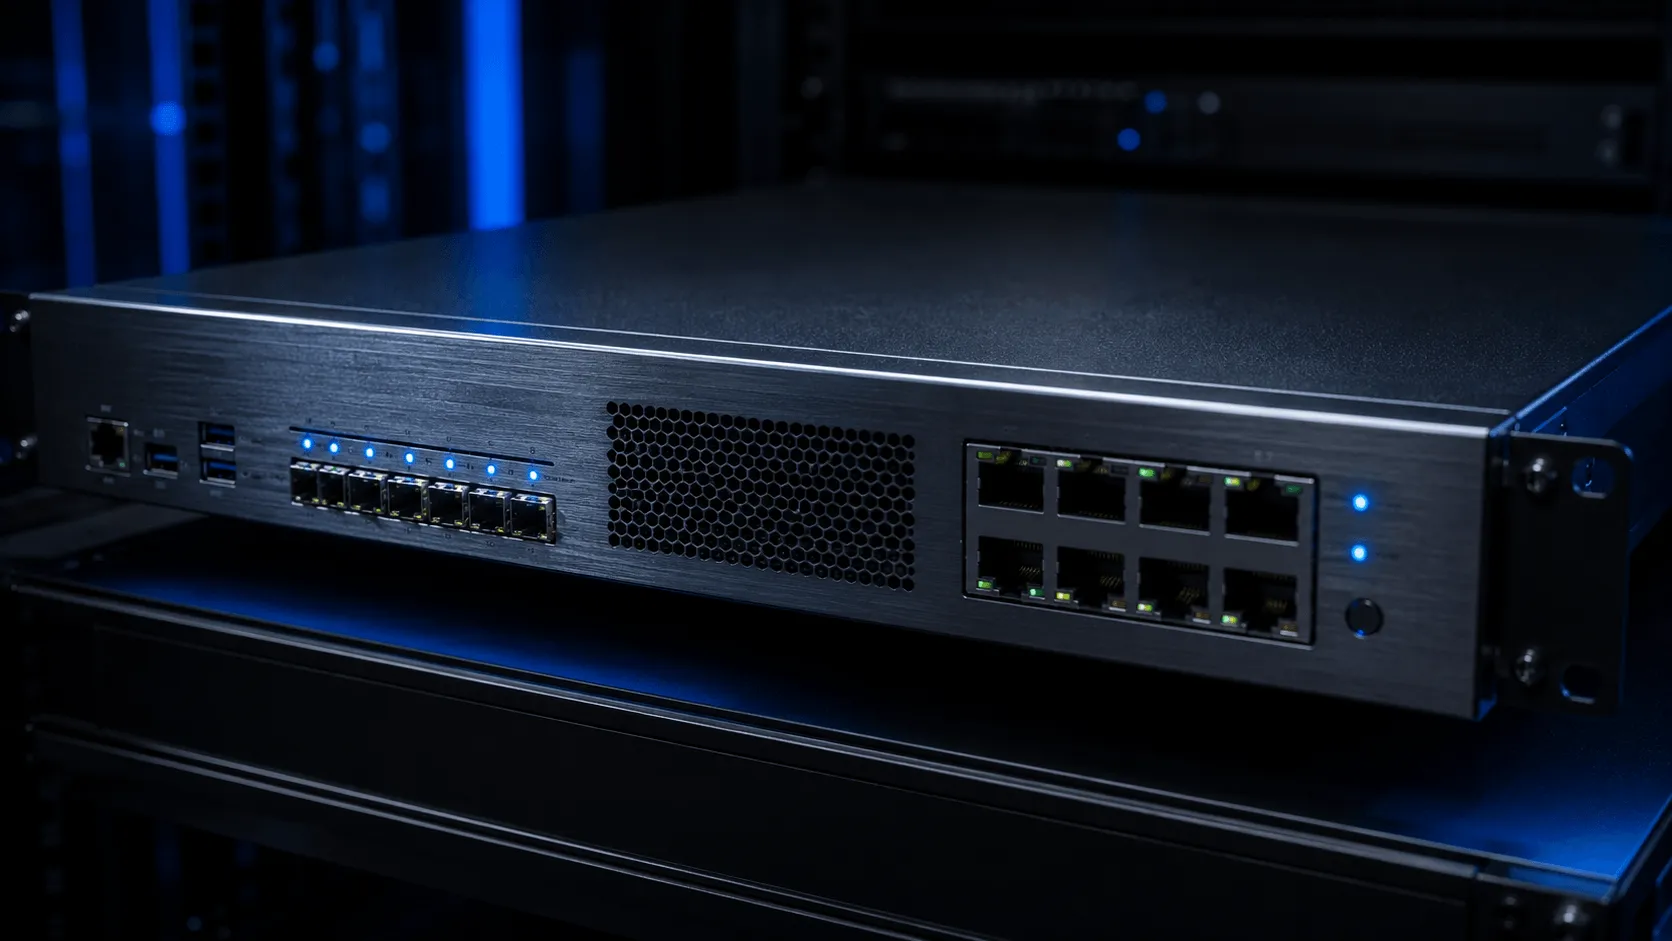
Reference system
Symptoms
When this matters
If any of these describe your environment, this is the conversation to have.
- 01The current firewall was sized for a smaller team or was never properly configured.
- 02Guest Wi-Fi, CCTV and core business systems all sit on the same trust zone.
- 03Remote staff connect back to the office without a defined secure-access method.
- 04Backup exists, but nobody has tested whether a restore actually works.
- 05Security subscriptions and licence renewals are tracked by nobody in particular.
Scope
What KINNEX delivers
Security is treated as an architecture decision, not a single appliance. KINNEX designs trust zones around how users, servers, CCTV and guests actually move through your network, so a compromise in one area does not become a compromise of everything.
- Next-generation firewall sizing, policy, web filtering, application control, VPN and reporting.
- Network segmentation for users, servers, CCTV, guest Wi-Fi, OT or sensitive systems.
- Endpoint protection, secure configuration, patching and identity controls.
- ZTNA or secure remote access, email security, backup and recovery readiness.
- Security posture reviews, incident readiness and remediation planning.
- Licensing and renewal visibility — an active SOC or round-the-clock monitoring is only implied when contracted and staffed.
Capability catalogue
Everything this covers
157 capabilities, scoped, sourced and delivered under one contract. Search for the exact term you use.
157 capabilities
Assess and audit20
Know where you stand before you spend. Scope, test, report, remediate.
- Vulnerability assessment (VA): network, web, API, mobile and cloud configuration
- Authenticated and unauthenticated scanning, with risk-rated reports
- Penetration testing (VAPT): black-box, grey-box and white-box
- Internal and external perimeter penetration testing
- Web application, mobile app and API penetration testing (OWASP Top 10, ASVS)
- Wireless penetration testing and rogue access point hunts
- Red team and assumed-breach exercises; purple-team collaboration
- Social engineering and phishing simulation
- Active Directory and Entra ID security assessment
- Secure configuration review against CIS Benchmarks
- Firewall rule-base audit and cleanup
- Source-code review: SAST, DAST and software composition analysis
- Cloud security posture review (AWS, Azure, GCP) and tenant hardening
- Architecture review, threat modelling (STRIDE, PASTA) and zero-trust readiness
- Security maturity assessment against NIST CSF 2.0 and CIS Controls v8
- Third-party and vendor risk assessment
- Business impact analysis and risk register
- Mock audits and audit-evidence preparation
- Virtual CISO (vCISO) advisory and board-level reporting
- Policy authoring: information security, acceptable use, access, BYOD, incident response, retention
Governance, risk and compliance (GRC)18
Designs and procedures aligned to the frameworks your regulator, customer or auditor asks for.
- ISO/IEC 27001 ISMS implementation and readiness
- ISO/IEC 27701 privacy and ISO 22301 business continuity readiness
- SOC 2 Type I and Type II readiness and audit support
- PCI-DSS scoping, segmentation and remediation
- HIPAA safeguards for health data and PHI handling
- GDPR gap analysis and data-protection practices
- India DPDP Act 2023 readiness: notices, consent, data mapping, breach process
- IT Act and IT Rules compliance practices
- CERT-In directions: incident reporting readiness, log retention and time synchronisation
- RBI cyber-security framework and IT governance directions
- SEBI CSCRF and IRDAI information-security guidelines
- NIST CSF, NIST SP 800-53 and CIS control mapping
- IT general controls (ITGC) and internal-audit support
- Record of processing activities (ROPA) and data-protection impact assessments
- DPO-as-a-service and privacy operations
- GRC platform setup and audit-evidence automation
- Cyber-insurance readiness: control evidence and questionnaires
- Sector regulator and customer-audit response support
Network and perimeter security19
Next-generation firewalls and the controls around them, tuned to your applications.
- Next-generation firewall (NGFW) and unified threat management (UTM)
- Application control, intrusion prevention (IPS, IDS) and anti-malware
- SSL and TLS inspection and certificate management
- URL, web and DNS filtering and secure web gateway (SWG)
- Sandboxing for unknown files and zero-day threats
- Site-to-site IPsec and remote-access SSL VPN
- Zero-trust network access (ZTNA), SASE and SSE
- Secure SD-WAN for multi-site networks
- High availability: active-active and active-passive clusters
- Rule-base optimisation, shadow-rule removal and change control
- Network segmentation and micro-segmentation
- DMZ design, jump hosts and bastion access
- Network access control (NAC) and 802.1X
- DDoS protection and web application firewall (WAF)
- Network detection and response (NDR) and IDS tooling
- Wireless intrusion detection and prevention
- Deception technology and honeypots
- Threat-intelligence feeds and geo-blocking
- Vendor and third-party remote access with session control
Endpoint and server protection15
- Endpoint protection platform (EPP) and next-generation antivirus
- Endpoint detection and response (EDR), XDR and MDR
- Ransomware protection and rollback
- Application control and allow-listing
- Device and USB control, and removable-media policy
- Disk encryption: BitLocker, FileVault and Linux LUKS
- Patch management and endpoint vulnerability management
- Local-administrator removal and LAPS
- Server hardening to CIS Benchmarks
- Workload protection for virtual and cloud servers (CWPP)
- File-integrity monitoring (FIM)
- Anti-exploit, browser isolation and sandboxing
- Mobile threat defence for Android and iOS
- VDI and remote-desktop security
- Centralised management console and policy baselines
Email, web and data protection15
- Email security gateway: anti-spam, anti-phishing and anti-malware
- Sandboxing, URL rewriting and time-of-click protection
- Business email compromise (BEC) and impersonation defence
- SPF, DKIM and DMARC setup and monitoring
- Email encryption (TLS, S/MIME), archiving and journaling
- Data loss prevention (DLP): endpoint, network, email and cloud
- OCR and content inspection, with policy-based controls
- Data discovery, classification and labelling
- Rights management (IRM) and secure document sharing
- Cloud access security broker (CASB) and SaaS controls
- Database activity monitoring, masking and tokenisation
- Encryption at rest and in transit; key management and HSMs
- Secrets management and certificate lifecycle
- Insider-risk monitoring and user-behaviour analytics (UEBA)
- E-discovery and legal-hold support
Identity and access management13
- Single sign-on (SSO) with SAML and OIDC
- Multi-factor authentication: authenticator apps, push, FIDO2, passkeys, hardware tokens
- Adaptive and conditional access policies
- Privileged access management (PAM): vaulting, rotation, session recording
- Just-in-time (JIT) and just-enough access
- Identity governance: joiner-mover-leaver, access reviews, role design (RBAC, ABAC)
- Active Directory cleanup, tiering and hardening
- Entra ID, Okta and Google identity configuration
- Self-service password reset and passwordless sign-in
- Smart cards, PKI and certificate-based authentication
- Service-account and machine-identity management
- Privileged remote access for vendors and contractors
- Directory services: LDAP, Kerberos and federation
Security operations and response19
Detection and response run as a managed service under an SOP and an SLA agreed with you. Coverage hours depend on the client and the contract.
- Security operations centre (SOC) monitoring with L1, L2 and L3 analysts
- Managed detection and response (MDR)
- SIEM: log ingestion, parsing, correlation rules and use-case authoring
- SOAR playbooks and automated response
- MITRE ATT&CK-aligned detection coverage
- Alert triage, escalation and tuning
- Threat intelligence: IOCs, TTPs and sector feeds
- Hypothesis-driven threat hunting and IOC sweeps
- Incident response: preparation, containment, eradication, recovery, lessons learned
- Incident-response retainer with pre-agreed hours
- Digital forensics: disk, memory, mobile, email and cloud
- Malware analysis and chain-of-custody handling
- Vulnerability-management programme: scan, prioritise (CVSS, EPSS), remediate, verify
- External attack-surface management and dark-web monitoring
- Breach and attack simulation and purple-team testing
- Phishing takedown and brand protection
- Security metrics: mean time to detect and respond, trends and dashboards
- Monthly health reports and quarterly review meetings
- Log retention and time-synchronisation practices designed for CERT-In directions
Cloud, application and DevSecOps10
- Cloud security posture management (CSPM) and CNAPP
- Container and Kubernetes security
- Infrastructure-as-code scanning and policy-as-code
- API security and web application firewall
- CI/CD pipeline security: SAST, DAST, SCA and SBOM
- Secrets scanning and rotation
- SaaS security posture management (SSPM) and shadow-IT discovery
- Microsoft 365 and Google Workspace hardening and secure-score improvement
- Cloud logging, monitoring and data-residency controls
- Secure software development lifecycle (SSDLC) advisory
OT, IoT and surveillance-network security8
- IT and OT segmentation using the Purdue model
- Industrial firewalls and unidirectional gateways
- Passive ICS and SCADA monitoring and asset discovery
- IEC 62443-aligned zone and conduit design
- Vendor remote access through jump hosts, with session recording
- Air-gap and removable-media hygiene
- CCTV, access-control and building-system network isolation
- Medical and IoT device segmentation
Resilience and recovery6
- Backup and business-continuity and disaster-recovery (BCDR) design
- Immutable and air-gapped backups, with offsite and cloud tiers
- RPO and RTO targets and commitments
- Ransomware recovery planning and clean-room restores
- Disaster-recovery drills and playbook authoring
- Business-continuity plan and crisis-communication templates
Awareness, training and exercises6
- Phishing simulations with follow-up training
- Role-based security awareness modules
- Tabletop exercises for leadership and IT
- Executive and board briefings
- Secure-coding training for developers
- Onboarding and offboarding security hygiene
Managed security operations8
- Firewall management: policy lifecycle, rule audits, firmware updates
- EDR, email-security and DLP platform management
- Quarterly vulnerability scans and penetration tests
- Configuration backup and change management
- Licence, subscription and renewal tracking
- OEM case handling and hardware replacement
- Escalation and reporting under an agreed SOP and SLA
- Annual security review and roadmap
Nothing listed under that term yet. If you need it, ask: we can usually source or deliver it through a specialist team. Tell us what you need.
The site, in 3D
A perimeter that inspects everything coming in
Next-generation firewalls at the edge, segmented networks inside, and monitoring that does not sleep.
- Firewall perimeter
- Segmentation
- Threat inspection
- Monitoring
Real-time 3D illustration of a typical site, not a specific client project.
Use cases
Where this shows up
Typical situations that lead an organisation to this work.
01
A business whose firewall has never been reviewed since initial installation.
02
An organisation isolating CCTV and guest Wi-Fi from core business systems for the first time.
03
A team moving from ad-hoc remote access to a managed secure-access solution.
Delivery method
How the work runs
Architecture before equipment. Validation before handover.
Stage 01 of 6
Assess
Posture review across network, endpoints, remote access and backup readiness.
Stage 02 of 6
Design
Firewall policy, segmentation plan and remote-access architecture.
Stage 03 of 6
Implement
Firewall deployment, endpoint rollout and secure remote-access configuration.
Stage 04 of 6
Validate
Policy testing, segmentation verification and backup restore tests.
Stage 05 of 6
Document
Trust-zone diagram, policy reference and renewal calendar.
Stage 06 of 6
Support
Ongoing licence and renewal management, plus periodic posture reviews.
How we take this on
One contract. The right specialist for every part
Your project is wider than any single team. We scope all of it, source all of it and carry the responsibility for all of it.
- 01
Scope
We survey, size and specify against standards and your operating reality, not against a brochure.
- 02
Source
Any make, any model, from the manufacturer, distribution or registered importers. GST-compliant invoicing, warranty and returns handled for you.
- 03
Deliver
KINNEX engineers do the work we do every day. Where a job needs a specialist, we bring in the right expert team as a sub-order under your single contract.
- 04
Own
One scope, one SOP, one SLA and one point of accountability, whoever is on site.
Standards and terms
Standards we design to, and the terms you will hear
Specifications are written against recognised standards. Here is the vocabulary, in plain language.
- ISO/IEC 27001, 27002, 27005, 27017, 27018, 27701
- ISO 22301 (business continuity)
- NIST CSF 2.0
- NIST SP 800-53, 800-61, 800-115, 800-207
- CIS Controls v8 and CIS Benchmarks
- MITRE ATT&CK
- OWASP Top 10 and ASVS
- PCI-DSS
- SOC 2 (AICPA Trust Services Criteria)
- HIPAA Security Rule
- GDPR
- India DPDP Act 2023
- IT Act 2000 and IT Rules
- CERT-In directions (2022)
- RBI cyber-security framework
- SEBI CSCRF
- IRDAI information-security guidelines
- IEC 62443 (industrial security)
- ITIL 4 service management
- CVSS and EPSS scoring
- VA vs VAPT
- A vulnerability assessment finds and ranks weaknesses. Penetration testing goes further and tries to exploit them, the way an attacker would.
- Red, blue and purple team
- Red teams attack, blue teams defend, purple teams work together so every attack improves a detection.
- NGFW
- A firewall that understands applications, users and threats, not just ports and addresses.
- EDR / XDR / MDR
- Detection and response on endpoints, extended across email, network and cloud, or run for you as a managed service.
- ZTNA
- Zero-trust network access: each user and device is verified for each application, instead of trusting anyone inside the network.
- SASE / SSE
- Security services delivered from the cloud, close to users and branches, replacing a stack of appliances.
- SIEM and SOAR
- SIEM collects and correlates logs to detect threats. SOAR automates the response with playbooks.
- SOC
- Security operations centre: the team and tooling that watch for threats and respond. Coverage hours are agreed per contract.
- DLP
- Data loss prevention: rules and tools that stop sensitive data leaving through email, USB, cloud or print.
- PAM
- Privileged access management: controlling, recording and rotating the most powerful accounts.
- MFA and passkeys
- A second proof of identity beyond a password. Passkeys and hardware keys resist phishing best.
- SPF, DKIM, DMARC
- Three DNS-based checks that prove an email really came from your domain, and tell receivers what to do with fakes.
- CSPM / CNAPP
- Tools that continuously check cloud accounts for misconfiguration and risk.
- CVSS and EPSS
- Scores for how severe a vulnerability is, and how likely it is to be exploited. Used together to decide what to patch first.
- MTTD and MTTR
- Mean time to detect and to respond: the two numbers that show whether security operations are improving.
- Purdue model
- A layered way to separate factory-floor networks from business IT, so a breach in one does not reach the other.
- BEC
- Business email compromise: fraud using a convincing email, often impersonating a director or supplier, to move money.
- Immutable backup
- A backup that cannot be altered or deleted for a set period, even by an administrator, which defeats ransomware.
- RPO and RTO
- How much data you can afford to lose, and how long you can afford to be down. They set the backup and recovery design.
- IR retainer
- A pre-agreed arrangement with an incident-response team and a pool of hours, so help starts without procurement delay.
- SOP and SLA
- The documented procedures for running security operations, and the response and reporting targets agreed for them.
Brands
Any make. Sourced, supplied and supported
We specify against your requirement and standards, then source the right product from the manufacturer, distribution or registered importers. Delivered, installed and supported under one contract.
Firewalls and network security
Next-generation firewalls, UTM, VPN, secure web and zero trust access.
 Sophos
 Fortinet
 Palo Alto Networks
 WatchGuard
 Barracuda Networks
 Cisco Secure
 Juniper Networks
 SonicWall
 Cloudflare
 pfSense
 OPNsense
%20--%3e%3csvg%20version='1.1'%20id='Layer_1'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%20390%20115'%20style='enable-background:new%200%200%20390%20115;'%20xml:space='preserve'%3e%3cstyle%20type='text/css'%3e%20.st0{fill:%2328A505;}%20%3c/style%3e%3cg%3e%3cg%3e%3cg%3e%3cpath%20class='st0'%20d='M49.3,20.8c0.2,0,0.4,0.2,0.4,0.4v9.6c0,0.2-0.2,0.4-0.4,0.4H14.4c-0.2,0-0.4,0.2-0.4,0.4v42.3%20c0,0.2-0.2,0.4-0.4,0.4H4c-0.2,0-0.4-0.2-0.4-0.4V21.2c0-0.2,0.2-0.4,0.4-0.4C4,20.8,49.3,20.8,49.3,20.8z%20M26.4,42.4%20c-0.3-0.3-0.6,0-0.6,0.3v29.6c0,0.5,0.3,0.6,0.6,0.2l15.2-14.1c0.2-0.2,0.2-0.5,0-0.7L26.4,42.4z'/%3e%3cpath%20d='M80,51.7H64.1v5.7h13.2c0.4,0,0.6,0.2,0.6,0.5c0,3.7,0,5,0,5.8c0,0.4-0.2,0.5-0.6,0.5H64.1c0,0,0,6.3,0,9.4%20c0,0.5,0,0.6-0.4,0.6h-7c-0.3,0-0.3,0-0.3-0.6c0-8.2,0-18.5,0-28c0-0.5,0-0.6,0.3-0.6H80c0.3,0,0.3,0.4,0.3,0.4v5.8%20C80.4,51.4,80.4,51.7,80,51.7z%20M113.7,59.8c0-8.4-6.6-15.3-15.3-15.3s-15.3,6.8-15.3,15.3c0,8.4,6.6,15.2,15.3,15.2%20S113.7,68.2,113.7,59.8z%20M105.7,59.8c0,4.4-2.7,7.9-7.2,7.9c-4.6,0-7.2-3.4-7.2-7.9c0-4.4,2.6-7.9,7.2-7.9%20C103,51.8,105.7,55.3,105.7,59.8z%20M144,73.1c-2.5-4-4.9-8.4-6.1-10.1c2.6-1.2,4-4,4-8c0-5.3-3.5-9.8-10.1-9.8h-13.3%20c-0.1,0-0.3,0-0.3,0.4c0,10.3,0,17.3,0,28.4c0,0.4,0,0.4,0.3,0.4c2.6,0,4.3,0,7,0c0.3,0,0.3,0,0.3-0.4c0-3.4,0-8.1,0-8.1l4.9-0.1%20c0,0,3.1,4.9,4.6,7.7c0.4,0.8,0.6,0.9,0.9,0.9h7.6C144.4,74.2,144.5,73.9,144,73.1z%20M133.8,55.5c0,2.5-1.3,4.2-3.6,4.3l-4.3,0.1%20v-8.4h4.3C132.6,51.5,133.8,53.2,133.8,55.5z%20M161.2,75.1c8.1,0,13-5.6,14-10.9c0.1-0.5,0-0.6-0.2-0.6h-7c-0.3,0-0.4,0.2-0.4,0.3%20c-1.3,2.6-3.3,3.8-6.2,3.8c-4.3,0-7-3.4-7-8v0.1c0-4.6,2.8-8,7-8c3,0,5,1.2,6.2,3.8c0,0.1,0.1,0.3,0.4,0.3h7%20c0.2,0,0.3-0.1,0.2-0.6c-1.1-5.3-5.9-10.9-14-10.9c-8.4,0-15,6.5-15,15.3C146.2,68.6,152.8,75.1,161.2,75.1z%20M200.3,73.6%20c0-1.8,0-3.4,0-5.5c0-0.5-0.1-0.6-0.6-0.6h-12.5v-4.9h12c0.4,0,0.4-0.1,0.4-0.6c0-1.7,0-3.1,0-5.2c0-0.5,0-0.6-0.4-0.6h-12v-4.9%20h12.3c0.3,0,0.5-0.1,0.5-0.5c0-1.9,0-3.1,0-5.2c0-0.5,0-0.6-0.5-0.6h-19.4c-0.4,0-0.4,0-0.4,0.4c0,8.3,0,20.6,0,28.1%20c0,0.5,0,0.6,0.5,0.6h19.7C200.3,74.2,200.3,74.2,200.3,73.6z%20M232.9,56.3c0-6.6-3.8-11.2-10.2-11.2H207c-0.2,0-0.4,0-0.4,0.4%20c0,10.3,0,17.3,0,28.4c0,0.4,0,0.4,0.4,0.4c2.5,0,4.3,0,7,0c0.3,0,0.4,0,0.4-0.4c0-3.4,0-7.1,0-7.1s7.7,0.2,8.9,0%20C228.8,66.1,232.9,63.3,232.9,56.3z%20M225,56c0,2.4-1.2,4.3-4.2,4.5h-6.4v-9h6.3C223.3,51.5,225,53.1,225,56z%20M267,59.8%20c0-8.4-6.6-15.3-15.3-15.3s-15.3,6.8-15.3,15.3c0,8.4,6.6,15.2,15.3,15.2S267,68.2,267,59.8z%20M258.9,59.8c0,4.4-2.7,7.9-7.2,7.9%20c-4.6,0-7.2-3.4-7.2-7.9c0-4.4,2.6-7.9,7.2-7.9C256.3,51.8,258.9,55.3,258.9,59.8z%20M279.2,73.9c0-6.8,0-21.7,0-28.4%20c0-0.3,0-0.4-0.4-0.4c-2.8,0-4.4,0-7.1,0c-0.4,0-0.4,0-0.4,0.4c0,10.3,0,17.3,0,28.4c0,0.4,0,0.4,0.4,0.4c2.7,0,4.3,0,7.1,0%20C279.2,74.2,279.2,74.2,279.2,73.9z%20M340,52.4c0-2.4,0-4,0-6.9c0-0.3,0-0.4-0.3-0.4h-25c-0.3,0-0.3,0.1-0.3,0.4%20c0,2.9,0,4.5,0,6.9c0,0.3,0,0.3,0.3,0.3l8.7-0.1c0,0,0,15.9,0,21.2c0,0.4,0,0.4,0.4,0.4c2.7,0,4.2,0,7.1,0c0.3,0,0.4,0,0.4-0.4%20c0-3.4,0-21.2,0-21.2l8.5,0.1C339.9,52.7,340,52.7,340,52.4z%20M309.9,73.2v-4.1c0-7.8,0-16.5,0-23.5c0-0.4,0-0.5-0.4-0.5%20c-2.7,0-4,0-6.5,0c-0.3,0-0.3,0-0.3,0.5v13.7c0,0-10.7-9.8-15.8-13.8c-1.3-1.1-1.4,0.1-1.4,0.5v0.1v4.1l0,0c0,8.5,0,14.3,0,23.6%20c0,0.2,0.1,0.4,0.4,0.4c2.6,0,3.8,0,6.5,0c0.4,0,0.4,0,0.4-0.4V61.2c0,0,8.8,7.4,15.3,12.3C309.7,75,309.9,74,309.9,73.2z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/svg%3e) Forcepoint
 Netgear
 Huawei
 Ubiquiti
 Tailscale
 OpenVPN
 WireGuard
Show 14 more brands
 Array Networks
 Kerio
- Cisco Umbrella
 Akamai
 Imperva
 F5
 Radware
- Check Point
- Zscaler
- Cato Networks
- Netskope
- Versa Networks
- Stormshield
- Untangle
Endpoint protection, EDR and XDR
Antivirus, EDR, XDR, MDR and ransomware protection.
 SentinelOne
 CrowdStrike
- Sophos
 Trend Micro
 Microsoft Defender
 Bitdefender
%20--%3e%3csvg%20version='1.1'%20id='Layer_1'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%20182%2071.9'%20style='enable-background:new%200%200%20182%2071.9;'%20xml:space='preserve'%3e%3cstyle%20type='text/css'%3e%20.st0{clip-path:url(%23SVGID_2_);fill:%230094A1;}%20.st1{clip-path:url(%23SVGID_2_);fill:%23FFFFFF;}%20%3c/style%3e%3cg%3e%3cdefs%3e%3crect%20id='SVGID_1_'%20y='0'%20width='182'%20height='71.9'/%3e%3c/defs%3e%3cclipPath%20id='SVGID_2_'%3e%3cuse%20xlink:href='%23SVGID_1_'%20style='overflow:visible;'/%3e%3c/clipPath%3e%3cpath%20class='st0'%20d='M175,2.8c0-0.1,0-0.1,0-0.2c0-0.1-0.1-0.1-0.2-0.2c-0.1,0-0.2-0.1-0.2-0.1c-0.1,0-0.2,0-0.3,0H174v1h0.2%20c0.2,0,0.3,0,0.4,0c0.1,0,0.2-0.1,0.3-0.1c0.1,0,0.1-0.1,0.1-0.2C175,3,175,2.9,175,2.8%20M176.6,5.4h-1.2l-1.1-1.3H174v1.3h-0.9V1.8%20h1.4c0.3,0,0.5,0,0.6,0c0.2,0,0.3,0.1,0.5,0.2c0.2,0.1,0.3,0.2,0.4,0.3c0.1,0.1,0.1,0.3,0.1,0.5c0,0.3-0.1,0.5-0.2,0.7%20c-0.1,0.2-0.3,0.3-0.6,0.4L176.6,5.4z%20M177.4,3.7c0-0.8-0.3-1.5-0.8-2c-0.6-0.6-1.2-0.9-2-0.9c-0.8,0-1.5,0.3-2,0.9%20c-0.6,0.6-0.8,1.2-0.8,2c0,0.8,0.3,1.5,0.8,2c0.6,0.6,1.2,0.9,2,0.9c0.8,0,1.5-0.3,2-0.9C177.1,5.1,177.4,4.5,177.4,3.7%20M178.2,3.7%20c0,1-0.4,1.9-1.1,2.6c-0.7,0.7-1.6,1.1-2.6,1.1c-1,0-1.9-0.4-2.6-1.1c-0.7-0.7-1.1-1.6-1.1-2.6c0-1,0.4-1.9,1.1-2.6%20c0.7-0.7,1.6-1.1,2.6-1.1c1,0,1.9,0.4,2.6,1.1C177.9,1.8,178.2,2.7,178.2,3.7'/%3e%3cpath%20class='st0'%20d='M25.1,3.7c-9,0-16.7,4.7-20.8,11.3C0.8,21.2,0,31.2,0,37.8c0,6.6,0.8,16.7,4.3,22.8c4,6.6,11.7,11.3,20.8,11.3%20h131.8c9,0,16.7-4.7,20.8-11.3c3.5-6.1,4.3-16.2,4.3-22.8c0-6.6-0.8-16.7-4.3-22.8c-4-6.6-11.7-11.3-20.8-11.3H25.1z'/%3e%3cpath%20class='st1'%20d='M112.8,34.1h11.1v-0.3c0-5.1-2-5.4-5.7-5.4C113.7,28.3,112.9,29.7,112.8,34.1%20M34.9,28.6%20c3.6,0,5.6,0.4,5.6,5.3v0.2H29.6C29.7,29.9,30.6,28.6,34.9,28.6%20M19.5,38c0,11.9,3,16.2,15.6,16.2c4.7,0,8.5-0.4,11.3-1.9%20c2.6-1.5,4.2-4.1,4.2-8.8h-9.9c-0.1,3.4-2.4,3.8-5.6,3.8c-4.6,0-5.5-1.9-5.5-7.6v-0.2h21V38c0-13-3.5-16.3-15.5-16.3%20C22.3,21.7,19.5,25.7,19.5,38%20M57.3,32.1c0,6.4,2.2,9.3,15.6,9.3c1.2,0,3.1-0.1,4.2,0.4c1,0.5,1.5,1.4,1.5,3c0,2.8-1,3.1-5.8,3.1%20c-2.6,0-5.3-0.1-5.5-3.6H57.3c0.1,7,3.4,9.3,9.6,9.8c1.9,0.1,3.9,0.1,6,0.1c8.5,0,15.6-1.4,15.6-10.6c0-8.8-4.6-9.4-15.6-9.7%20c-5.5-0.1-5.8-1.3-5.8-3.1c0-2.1,0.2-2.8,5.8-2.8c2,0,4.1,0.2,4.5,2.7h9.5v-1.3c0-7.6-8-7.7-14-7.7C63.8,21.7,57.3,21.9,57.3,32.1%20M140.1,21.7h24.8V29h-7.4v24.9h-10.1V29h-7.4V21.7z%20M102.9,37.8c0-12.3,2.7-16.2,15.5-16.2c11.9,0,15.4,3.2,15.4,16.2v1.4h-21v0.3%20c0,5.7,0.9,7.7,5.6,7.7c3.1,0,5.5-0.3,5.7-3.8h9.7c-0.1,4.5-1.6,7.1-4.2,8.6c-2.7,1.5-6.5,1.9-11.2,1.9%20C105.9,53.9,102.9,49.7,102.9,37.8%20M12.2,59.9C7.1,54.4,6,45.9,6,37.8c0-8.1,1.1-16.6,6.2-22.1c3.2-3.4,9.4-6,14.6-6h67.9v56.2%20H26.8C21.5,65.9,15.4,63.3,12.2,59.9'/%3e%3c/g%3e%3c/svg%3e) ESET
 Kaspersky
 Symantec
;}.cls-2{fill:%231a1a1a;}%3c/style%3e%3cradialGradient%20id='radial-gradient'%20cx='856.63'%20cy='123.19'%20r='182.23'%20gradientUnits='userSpaceOnUse'%3e%3cstop%20offset='0.07'%20stop-color='%232814ff'/%3e%3cstop%20offset='0.08'%20stop-color='%232718ff'/%3e%3cstop%20offset='0.23'%20stop-color='%231654ff'/%3e%3cstop%20offset='0.35'%20stop-color='%230a80ff'/%3e%3cstop%20offset='0.45'%20stop-color='%23039bff'/%3e%3cstop%20offset='0.5'%20stop-color='%2300a5ff'/%3e%3cstop%20offset='1'%20stop-color='%2300cd00'/%3e%3c/radialGradient%3e%3c/defs%3e%3cpath%20class='cls-1'%20d='M904.59,122.12H852.4L947.81,0H1000Z'/%3e%3cpath%20class='cls-2'%20d='M76.75,43.61H0V0H197.47V43.61h-74v204.1H76.75Z'/%3e%3cpath%20class='cls-2'%20d='M197.47,62.8h45.35V90.36q8.72-15.7,26.17-23.9T311.9,62.1v48.5q-17.1-5.94-33.14-2.27a45.92,45.92,0,0,0-26,15.7q-9.93,12-9.94,29.48v94.2H197.47Z'/%3e%3cpath%20class='cls-2'%20d='M415.6,250.5a95,95,0,0,1-95.25-95.25,93.3,93.3,0,0,1,12.91-48.14,95.16,95.16,0,0,1,34.89-34.72A93.13,93.13,0,0,1,415.6,59.66,91.49,91.49,0,0,1,458,69.78a96.12,96.12,0,0,1,33.14,27.91,94.44,94.44,0,0,1,17.62,39.42A84.24,84.24,0,0,1,509.1,172H365.36A46.77,46.77,0,0,0,375,192.93,44.27,44.27,0,0,0,392.75,206a59.37,59.37,0,0,0,22.85,4.36,69.9,69.9,0,0,0,26-5.05,60,60,0,0,0,21.46-14.13L502.82,202q-11.18,22-35.94,35.24T415.6,250.5Zm49.19-113a49.21,49.21,0,0,0-9.25-18.84,48.41,48.41,0,0,0-17.09-13.78,51.94,51.94,0,0,0-23.2-5.06,53.07,53.07,0,0,0-23.38,5.06,48.17,48.17,0,0,0-17.27,13.78,49.19,49.19,0,0,0-9.24,18.84Z'/%3e%3cpath%20class='cls-2'%20d='M531.69,0h45V247.71h-45Z'/%3e%3cpath%20class='cls-2'%20d='M610.05,0h45V247.71h-45Z'/%3e%3cpath%20class='cls-2'%20d='M686.55,62.8h45V247.71h-45Z'/%3e%3cpolygon%20class='cls-2'%20points='951.24%20247.66%20806.74%2062.8%20754.55%2062.8%20826.77%20155.19%20754.55%20247.66%20806.74%20247.66%20852.88%20188.59%20899.05%20247.66%20951.24%20247.66'/%3e%3c/svg%3e) Trellix
 VMware Carbon Black
 Malwarebytes
%20--%3e%3csvg%20version='1.1'%20id='Layer_1'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%201000%20266.4'%20style='enable-background:new%200%200%201000%20266.4;'%20xml:space='preserve'%3e%3cstyle%20type='text/css'%3e%20.st0{fill:%230D2345;}%20%3c/style%3e%3cg%3e%3cpath%20class='st0'%20d='M172.5,50.7h25l65.7,157.4h-24.1l-11.3-28.7h-85.4l-11.6,28.7h-24.1L172.5,50.7z%20M219.9,159.7l-7.4-18.1h-55.1%20l-7.2,18.1H219.9z%20M205.3,123.1l-4.2-10.2c-6.7-16.7-12.5-30.6-16.2-41c-3.5,10.4-9.3,24.3-16,41l-4.2,10.2H205.3z%20M265.1,147%20c0-37.7,27.8-63.4,63.7-63.4c30.8,0,54.2,17.6,59.5,47.9h-23.8c-5.3-18.7-18.1-27.1-36.1-27.1c-25.2,0-39.6,18.5-39.6,42.6%20c0,25.2,15.3,42.6,39.8,42.6c17.8,0,31-9,36.1-25.2h23.8c-7.4,29.6-31,46.1-60.9,46.1C289.1,210.4,265.1,183.5,265.1,147z%20M406.2,85.9h21.3l0.9,15.5c7.6-10.9,19-17.8,33.3-17.8h2.1v25.7h-3.5c-24.3,0-31,13.9-31,35.6v63.2h-23.1V85.9z%20M467.6,147%20c0-37.5,28-63.4,64.1-63.4c37.5,0,64.1,27.3,64.1,63.4c0,36.6-27.1,63.4-64.1,63.4S467.6,183.5,467.6,147z%20M572.2,146.7%20c0-24.1-15.7-42.4-40.5-42.4c-25.2,0-40.3,18.5-40.3,42.4c0,25.5,16.9,42.8,40.5,42.8C555.8,189.5,572.2,171.3,572.2,146.7z%20M612.9,85.9h20.6l1.6,12.7c9.5-9.9,22.4-15,39.1-15c28.9,0,45.1,17.1,45.1,47.4v77.1h-23.1v-72.7c0-19.9-7.9-30.8-26.9-30.8%20c-20.6,0-33.3,13.2-33.3,33.1v70.4h-23.1V85.9z%20M744.6,85.9h22.9v122.2h-22.9V85.9z%20M791.4,170.3h22.5%20c2.3,14.8,14.1,21.3,31.5,21.3c14.4,0,25.2-5.6,25.2-16.9c0-7.9-3.7-11.1-9.5-13.2c-5.6-2.1-11.3-3-22.9-4.9%20c-12-1.8-20.4-3.7-27.6-7.2c-11.1-5.3-15.5-15.3-15.5-26.4c0-25.9,20.4-39.6,46.5-39.6c28.5,0,47.4,13.2,48.8,39.8h-22%20c-1.4-14.1-12.5-21.1-26.8-21.1c-15.3,0-24.3,7.6-24.3,18c0,6.7,3.2,10.2,9.3,12.5c6,2.3,17.1,3.5,26.6,4.9c9,1.4,17.4,3,25,7.2%20c10.2,5.5,15,16.2,15,27.1c0,11.6-4.4,21.8-12.7,28.5c-8.8,7.2-20.4,10-35.2,10C815.5,210.4,793.7,199.3,791.4,170.3z'/%3e%3c/g%3e%3c/svg%3e) Acronis
 McAfee
 Webroot
 Broadcom
 Elastic
- Cisco Secure Endpoint
Show 10 more brands
 Avast
 G DATA
- Quick Heal
- Seqrite
- Cybereason
- Cynet
- Huntress
- Arctic Wolf
- Tanium
- F-Secure
Email security and data loss prevention
Anti-phishing, sandboxing, encryption, archiving and DLP.
%20--%3e%3csvg%20version='1.1'%20id='layer'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%20652%20652'%20style='enable-background:new%200%200%20652%20652;'%20xml:space='preserve'%3e%3cstyle%20type='text/css'%3e%20.st0{fill:%23231F20;}%20%3c/style%3e%3cg%20id='Layer_2'%3e%3cg%20id='Layer_1-2'%3e%3cpath%20class='st0'%20d='M597.7,352.5v-12.8h-4.4c-4.8,0-5.9-0.7-5.9-4.1v-35.2h10.4v-11.9h-10.4v-17.3h-17.8v17.3h-8.9v11.9h8.9v34.3%20c0,13.3,3.2,18.1,18,18.1C589.4,352.9,592.8,352.6,597.7,352.5'/%3e%3cpath%20class='st0'%20d='M495.5,352.1h18v-37.7c0-8.4,5.4-13.4,13.8-13.4c7.7,0,10.4,4.1,10.4,12.7v38.4h18v-43.3%20c0-14.6-7.3-21.9-22.1-21.9c-8.5,0-15.3,3.1-20.4,9.2v-7.5h-17.6V352.1z'/%3e%3crect%20x='466.5'%20y='266.1'%20class='st0'%20width='18'%20height='15.4'/%3e%3crect%20x='466.5'%20y='288.5'%20class='st0'%20width='18'%20height='63.5'/%3e%3cpath%20class='st0'%20d='M409.7,320.2c0-12.7,5.8-19.6,15.8-19.6c10,0,15.7,6.9,15.7,19.6c0,12.7-5.7,19.7-15.7,19.7%20S409.7,332.9,409.7,320.2%20M391.5,320.2c0,21.2,12.9,34,34,34s34-12.8,34-34c0-21.2-12.9-34-34-34S391.5,299,391.5,320.2'/%3e%3cpath%20class='st0'%20d='M367.9,320.7c0,11.8-5.7,18.8-14.5,18.8c-9.5,0-15-6.7-15-18.8c0-13,5.2-19.7,14.7-19.7%20C362.4,301,367.9,307.8,367.9,320.7%20M320.8,377.5h17.5v-33.4c4.4,6.6,11.3,10,19.9,10c15.7,0,27.6-13.3,27.6-34.2%20c0-20.3-11.6-33.6-27.8-33.6c-8.7,0-14.8,3.4-20,10.8v-8.6h-17.1V377.5z'/%3e%3cpath%20class='st0'%20d='M284.3,352.1h17.6v-51.6H313v-11.9h-11.3v-4.4c0-4.1,1.6-4.8,6.6-4.8h4.7v-13.5c-3.2-0.2-5.9-0.4-8.6-0.4%20c-13.8,0-20.1,5.3-20.1,17.2v5.9h-9.6v11.9h9.6L284.3,352.1z'/%3e%3cpath%20class='st0'%20d='M223.8,320.2c0-12.7,5.8-19.6,15.8-19.6c10,0,15.7,6.9,15.7,19.6c0,12.7-5.7,19.7-15.7,19.7%20C229.6,340,223.8,332.9,223.8,320.2%20M205.6,320.2c0,21.2,12.9,34,34,34c21.1,0,34-12.8,34-34c0-21.2-12.9-34-34-34%20C218.4,286.3,205.5,299.1,205.6,320.2'/%3e%3cpath%20class='st0'%20d='M151.6,320.2c0-12.7,5.8-19.6,15.8-19.6s15.7,6.9,15.7,19.6c0,12.7-5.7,19.7-15.7,19.7%20S151.6,332.9,151.6,320.2%20M133.4,320.2c0,21.2,12.9,34,34,34s34-12.8,34-34s-12.9-34-34-34S133.4,299.1,133.4,320.2'/%3e%3cpath%20class='st0'%20d='M92.7,352.1h18v-33.6c0-9.6,5.1-14.4,14.8-14.4h5.9v-17.2c-0.9-0.1-1.8-0.1-2.7-0.1%20c-8.6,0-14.7,3.9-19.4,12.7v-10.9H92.7V352.1z'/%3e%3cpath%20class='st0'%20d='M67.6,320.7c0,11.8-5.7,18.8-14.5,18.8c-9.5,0-15-6.7-15-18.8c0-13,5.2-19.7,14.7-19.7S67.7,307.8,67.6,320.7%20M20.6,377.5H38v-33.4c4.4,6.6,11.3,10,19.9,10c15.7,0,27.6-13.3,27.6-34.2c0-20.3-11.6-33.6-27.8-33.6c-8.7,0-14.8,3.4-20,10.8%20v-8.6H20.6V377.5z'/%3e%3cpath%20class='st0'%20d='M620.6,346.8c0.1,3.9-2.9,7.1-6.8,7.2c-3.9,0.1-7.1-2.9-7.2-6.8c-0.1-3.9,2.9-7.1,6.8-7.2c0.1,0,0.2,0,0.3,0%20C617.4,339.9,620.5,343,620.6,346.8C620.6,346.8,620.6,346.8,620.6,346.8z%20M608.3,346.8c-0.1,2.9,2.2,5.4,5.1,5.5%20c0.1,0,0.1,0,0.2,0c2.9,0,5.2-2.4,5.2-5.2c0-0.1,0-0.1,0-0.2c0.1-2.9-2.1-5.4-5-5.5c-2.9-0.1-5.4,2.1-5.5,5%20C608.3,346.5,608.3,346.7,608.3,346.8L608.3,346.8z%20M612.5,350.4h-1.6v-6.8c0.9-0.2,1.7-0.2,2.6-0.2c0.8-0.1,1.6,0.1,2.4,0.5%20c0.4,0.4,0.7,0.9,0.7,1.5c-0.1,0.8-0.6,1.4-1.4,1.6v0.1c0.7,0.3,1.2,0.9,1.2,1.6c0.1,0.6,0.2,1.2,0.5,1.7h-1.7%20c-0.3-0.5-0.4-1.1-0.5-1.7c-0.1-0.8-0.5-1.1-1.4-1.1h-0.8L612.5,350.4z%20M612.5,346.5h0.8c0.9,0,1.6-0.3,1.6-1s-0.5-1-1.5-1%20c-0.3,0-0.6,0-0.9,0.1V346.5z'/%3e%3c/g%3e%3c/g%3e%3c/svg%3e) Proofpoint
- Barracuda Networks
- Sophos
- Forcepoint
- Trellix
- Symantec
%20--%3e%3csvg%20version='1.1'%20id='Layer_1'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%20500%20500'%20style='enable-background:new%200%200%20500%20500;'%20xml:space='preserve'%3e%3cstyle%20type='text/css'%3e%20.st0{fill:url(%23SVGID_1_);}%20.st1{fill:url(%23SVGID_00000078752512887004802280000005689619808096703373_);}%20.st2{fill:url(%23SVGID_00000000938455338878114860000005090300476476082311_);}%20.st3{fill:url(%23SVGID_00000062888845095373847610000015670046095858653342_);}%20%3c/style%3e%3clinearGradient%20id='SVGID_1_'%20gradientUnits='userSpaceOnUse'%20x1='249.37'%20y1='308.6733'%20x2='249.37'%20y2='200.05'%3e%3cstop%20offset='0'%20style='stop-color:%2329BADE'/%3e%3cstop%20offset='1'%20style='stop-color:%2350E6FF'/%3e%3c/linearGradient%3e%3cpath%20class='st0'%20d='M293.28,244.51c-24.56,0-44.48-19.9-44.51-44.46c-29.99,0.33-54.04,24.92-53.71,54.91%20c0.33,29.99,24.92,54.04,54.91,53.71c29.99-0.33,54.04-24.92,53.71-54.91c-0.04-3.45-0.4-6.88-1.09-10.26%20C299.53,244.16,296.41,244.5,293.28,244.51z'/%3e%3clinearGradient%20id='SVGID_00000075854636923193000240000013142184365114077320_'%20gradientUnits='userSpaceOnUse'%20x1='179.9192'%20y1='404.2232'%20x2='179.9192'%20y2='95.4182'%3e%3cstop%20offset='0.041'%20style='stop-color:%2332BEDD'/%3e%3cstop%20offset='0.495'%20style='stop-color:%2350E6FF'/%3e%3cstop%20offset='0.92'%20style='stop-color:%23C3F1FF'/%3e%3c/linearGradient%3e%3cpath%20style='fill:url(%23SVGID_00000075854636923193000240000013142184365114077320_);'%20d='M355.99,311.23%20c-1.99-19.58-8.13-38.52-18-55.55c-2.87,46.51-41.38,82.8-87.99,82.88c-2.11,0-4.09-0.47-6.15-0.63%20c-46.65-0.61-91.35-18.85-125.12-51.05c-29.03-27.89-50.56-62.66-62.6-101.08c-15.89,14.44-30.93,29.78-45.06,45.94%20c-10.12,9.37-10.74,25.17-1.37,35.29c0.44,0.48,0.9,0.93,1.37,1.37c30.37,36.42,66.16,67.97,106.1,93.53%20c40.17,27.53,87.73,42.27,136.43,42.29c31.65,0.18,62.88-7.25,91.06-21.65c1.78-0.82,3.32-1.92,5.08-2.74%20C355.98,357.54,358.1,334.28,355.99,311.23z'/%3e%3clinearGradient%20id='SVGID_00000118398247856370114850000009538093576200672444_'%20gradientUnits='userSpaceOnUse'%20x1='207.845'%20y1='278.7343'%20x2='207.845'%20y2='9.9709'%3e%3cstop%20offset='0.244'%20style='stop-color:%230078D4'/%3e%3cstop%20offset='0.6'%20style='stop-color:%232E8CE1'/%3e%3cstop%20offset='0.933'%20style='stop-color:%23589EED'/%3e%3c/linearGradient%3e%3cpath%20style='fill:url(%23SVGID_00000118398247856370114850000009538093576200672444_);'%20d='M172,291.17%20c-18.74-34.51-12.1-77.28,16.22-104.48c22.25-29.95,53.43-52.05,89.06-63.12c19.42-5.93,39.58-9.11,59.88-9.44%20c-16.34-7.08-33.44-12.24-50.96-15.37c-47.99-8.08-97.31,0.06-140.16,23.14c-23.97,12.44-46.6,27.32-67.51,44.41%20c9.87,37.68,29.79,71.97,57.63,99.21C146.9,275.63,158.96,284.26,172,291.17z'/%3e%3clinearGradient%20id='SVGID_00000142887456421092235290000000266993271742146961_'%20gradientUnits='userSpaceOnUse'%20x1='377.0232'%20y1='404.4025'%20x2='377.0232'%20y2='118.0746'%3e%3cstop%20offset='0'%20style='stop-color:%23005BA1'/%3e%3cstop%20offset='0.399'%20style='stop-color:%230078D4'/%3e%3cstop%20offset='0.857'%20style='stop-color:%235EA0EF'/%3e%3c/linearGradient%3e%3cpath%20style='fill:url(%23SVGID_00000142887456421092235290000000266993271742146961_);'%20d='M489.59,232.96%20c-26.82-32.13-57.79-60.54-92.1-84.5c-35.88-9.8-73.75-9.61-109.53,0.55c-10.74,3.28-21.13,7.68-30.93,13.17%20c15.33,1.08,30.11,6.15,42.87,14.71c1.14,0.33,2.24,0.82,3.24,1.45c42.69,28.67,71.46,73.89,79.34,124.71%20c2.51,19.72,2.2,39.68-0.91,59.31c40.67-25.85,77.07-57.85,107.91-94.88c9.56-8.9,10.1-23.87,1.19-33.43%20C490.32,233.67,489.96,233.31,489.59,232.96z'/%3e%3c/svg%3e) Microsoft Purview
- Trend Micro
- Cisco Secure Email
 Google Workspace
- Cloudflare
- Mimecast
- Netskope
- Safetica
- Digital Guardian
- Zscaler
- Ironscales
- Abnormal Security
Show 9 more brands
- KnowBe4
- Egress
- Virtru
- Varonis
- Titus
- Seclore
- Cyberhaven
- Tessian
- Hornetsecurity
Identity, MFA and privileged access
SSO, MFA, IAM, password vaulting and privileged session control.
 Okta
 BeyondTrust
 ARCON
- Microsoft Entra
 Ping Identity
 Thales
 Entrust
 Auth0
%20--%3e%3csvg%20version='1.1'%20id='Layer_2'%20xmlns='http://www.w3.org/2000/svg'%20xmlns:xlink='http://www.w3.org/1999/xlink'%20x='0px'%20y='0px'%20viewBox='0%200%20142.8%2035.2'%20enable-background='new%200%200%20142.8%2035.2'%20xml:space='preserve'%3e%3cpath%20fill='%231C1F2A'%20d='M47.3,15.9c0.3-2,2.1-4.5,5.5-4.5c3.2,0,5,2.3,5.3,4.5H47.3z%20M42.9,17.5c0,5.6,4.1,9.4,10,9.4%20c3.9,0,6.5-1.9,8-3.6c0.2-0.2,0.2-0.4,0-0.6l-2.1-1.9c-0.2-0.2-0.5-0.2-0.6,0c-1.1,0.9-2.7,2.4-5.2,2.4c-2.9,0-5-1.8-5.5-4.1h14.5%20c0.4,0,0.6-0.2,0.6-0.6v-0.9c0-5.4-3.5-9.8-9.4-9.8C46.7,7.8,42.9,12.1,42.9,17.5L42.9,17.5z%20M65.1,26.2c0,0.3,0.2,0.5,0.5,0.5h3.1%20c0.3,0,0.5-0.2,0.5-0.5V0.4C69.1,0.2,69,0,68.7,0h-3.2c-0.3,0-0.4,0.2-0.4,0.4V26.2z%20M36.5,26.2c0,0.3,0.2,0.5,0.5,0.5H40%20c0.3,0,0.5-0.2,0.5-0.5V15.8c0-4.4-2.6-8-8.1-8h-0.1c-2.7,0-4.7,0.9-5.9,1.9v-1c0-0.3-0.2-0.5-0.5-0.5h-3.1c-0.3,0-0.5,0.2-0.5,0.5%20v17.4c0,0.3,0.2,0.5,0.5,0.5h3.1c0.3,0,0.5-0.2,0.5-0.5v-9.6c0-3,1.5-5.2,5.1-5.2c3.6,0,5,2.2,5,5.2V26.2z%20M95,31.6%20c1.4,1.7,4.4,3.7,8.6,3.7c5.9,0,9.4-3.6,9.4-9.3V8.8c0-0.3-0.2-0.5-0.5-0.5h-2.9c-0.3,0-0.5,0.2-0.5,0.5v1c-1.3-1.1-3-1.9-5.8-1.9%20c-5.3,0-9.9,3.9-9.9,9.6c0,5.8,4.5,9.6,9.9,9.6c2.6,0,4.3-0.9,5.6-1.9v1.2c0,3.2-1.9,5.4-5.4,5.4c-2.9,0-4.8-1.6-6.1-2.8%20c-0.2-0.2-0.6-0.2-0.8,0L95,30.8C94.7,31,94.7,31.3,95,31.6L95,31.6z%20M15.6,17.4c0,3.2-2.4,5.8-5.7,5.8s-5.5-2.8-5.5-5.8v-0.2%20c0-3.1,2.3-5.7,5.5-5.7S15.6,14.1,15.6,17.4L15.6,17.4z%20M0,17.4C0,22.6,4.2,27,9.9,27s9.9-4.4,9.9-9.6v-0.2c0-5.2-4.2-9.4-9.9-9.4%20S0,12,0,17.4L0,17.4z%20M87.1,17.4c0,3.2-2.4,5.8-5.7,5.8c-3.2,0-5.5-2.8-5.5-5.8v-0.2c0-3.1,2.3-5.7,5.5-5.7%20C84.7,11.5,87.1,14.1,87.1,17.4L87.1,17.4z%20M71.5,17.4c0,5.2,4.2,9.6,9.9,9.6s9.9-4.4,9.9-9.6v-0.2c0-5.2-4.2-9.4-9.9-9.4%20S71.5,12,71.5,17.4L71.5,17.4z%20M116.8,26.2c0,0.3,0.2,0.5,0.5,0.5h3.1c0.3,0,0.5-0.2,0.5-0.5V8.7c0-0.2-0.1-0.4-0.4-0.4h-3.2%20c-0.3,0-0.4,0.2-0.4,0.4V26.2z%20M116.8,3.7c0,0.3,0.2,0.5,0.5,0.5h3.1c0.3,0,0.5-0.2,0.5-0.5V0.4c0-0.2-0.1-0.4-0.4-0.4h-3.2%20c-0.3,0-0.4,0.2-0.4,0.4V3.7z%20M138.7,26.2c0,0.3,0.2,0.5,0.5,0.5h3.1c0.3,0,0.5-0.2,0.5-0.5V15.8c0-4.4-2.6-8-8.1-8h-0.1%20c-2.7,0-4.7,0.9-5.9,1.9v-1c0-0.3-0.2-0.5-0.5-0.5h-3.1c-0.3,0-0.5,0.2-0.5,0.5v17.4c0,0.3,0.2,0.5,0.5,0.5h3.1%20c0.3,0,0.5-0.2,0.5-0.5v-9.6c0-3,1.5-5.2,5.1-5.2c3.6,0,5,2.2,5,5.2V26.2z%20M109,17.4c0,3.2-2.4,5.8-5.7,5.8s-5.5-2.8-5.5-5.8v-0.2%20c0-3.1,2.3-5.7,5.5-5.7S109,14.1,109,17.4z'/%3e%3c/svg%3e) OneLogin
 Keeper
 1Password
 Bitwarden
 LastPass
 RSA
 Yubico
 Teleport
 Zoho Vault
 Google Authenticator
Show 13 more brands
- Microsoft Authenticator
- CyberArk
- Ekran System
- Duo Security
- ForgeRock
- JumpCloud
- Delinea
- HashiCorp Vault
- SailPoint
- Saviynt
- Imprivata
- StrongDM
- ManageEngine PAM360
SIEM, SOC, vulnerability and testing tools
Log analytics, detection, vulnerability management, penetration testing and forensics.
 Splunk
- Microsoft Sentinel
 IBM QRadar
- Elastic
 Wazuh
 Graylog
 Sumo Logic
 Tenable
 Qualys
 Nessus
 Burp Suite
 Metasploit
%20--%3e%3cg%3e%3cg%20id='Layer_1'%3e%3cg%20id='fn46EB'%3e%3cg%3e%3cpath%20d='M226.96,402.66c-32.46-84.39-64.41-167.47-96.57-251.08,2.07-.15,3.48-.33,4.88-.33,18.33-.02,36.66.12,54.99-.12,3.75-.05,5.14,1.42,6.34,4.6,12.4,32.76,24.92,65.48,37.42,98.2.64,1.68,1.42,3.3,2.71,6.26,2.06-4.05,3.68-6.99,5.08-10.04,14.41-31.4,28.72-62.84,43.32-94.15,1.08-2.31,4.35-5.2,6.37-5.04,2.41.2,5.57,2.93,6.71,5.37,15.41,32.95,30.52,66.03,45.72,99.07.58,1.27,1.39,2.44,2.67,4.65,1.38-3.28,2.39-5.48,3.26-7.74,12.37-32.23,24.73-64.47,37.08-96.71.83-2.16,1.29-4.22,4.56-4.2,18.66.09,37.32-.05,55.99-.09.45,0,.89.24,1.73.49-.56,1.8-.98,3.54-1.62,5.2-30.98,80.58-61.98,161.16-93.05,241.71-.63,1.64-2.21,2.92-3.35,4.36-1.09-1.32-2.52-2.48-3.2-3.99-16.7-36.92-33.25-73.91-50.09-110.77-1.12-2.45-4.23-5.24-6.64-5.47-1.97-.19-5.17,2.75-6.33,5.06-18.17,35.87-36.09,71.86-54.08,107.81-.95,1.89-2.05,3.7-3.88,6.97Z'/%3e%3cpath%20d='M550.21,212.45v-59.73c2.24,0,4.2,0,6.16,0,60.16,0,120.31,0,180.47,0,.17,0,.33,0,.5,0,7.68.03,8.51,1.33,4.93,7.98-6.15,11.41-12.34,22.8-18.54,34.18-26.64,48.89-53.29,97.77-79.92,146.66-2.54,4.67-1.31,6.64,4.17,6.65,30.83.02,61.66.01,92.48.01,1.95,0,3.9,0,6.12,0v54.91h-5.58c-62.32,0-124.65,0-186.97,0-7.78,0-8.63-1.38-5.13-8.38,29.03-57.97,58.07-115.93,87.1-173.89,3.48-6.96,2.61-8.38-5.16-8.38-24.83-.01-49.66,0-74.49,0-1.96,0-3.92,0-6.14,0Z'/%3e%3cpath%20d='M526.68,402.84h-60.32v-249.84h60.32v249.84Z'/%3e%3cpath%20d='M785.45,161.15c-3.65-32.08-13.42-41.79-51.81-51.93,13.87-3.35,27.65-5.17,37.33-15.42,9.5-10.08,11.48-23.58,14.83-36.88,2.56,31.31,18.62,49.33,50.82,51.94-13.03,3.73-26.17,5.72-35.9,15.14-9.96,9.65-11.75,23.05-15.26,37.15Z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/svg%3e) Wiz
 Google Chronicle
 Shuffle
 Autopsy
 Wireshark
 Kali Linux
Show 23 more brands
 OWASP ZAP
 Checkmarx
 Snyk
 Mandiant
- LogRhythm
- Exabeam
- Rapid7
- OpenVAS
- Cobalt Strike
- Nmap
- Prisma Cloud
- Darktrace
- TheHive
- MISP
- Velociraptor
- Volatility
- FTK
- EnCase
- Acunetix
- Invicti
- SonarQube
- Recorded Future
- Group-IB
Product names, logos and brands are property of their respective owners and are used for identification only. Don't see what you need? We can usually source it, including through registered importers.Ask us.
Technology fit
The technology categories this work draws on.
- Next-generation firewall (NGFW) platforms
- Endpoint protection and patch management
- ZTNA and VPN secure remote-access gateways
- Backup and recovery platforms
Reading
Related insights
Cybersecurity and Firewalls
A security and IT checklist for bank branches and ATMs
Network, CCTV, vault access, alarms, logging and failover. What a standard branch design covers, and how to keep many branches consistent.
Cybersecurity and Firewalls
Firewall renewals and end-of-life: plan before support lapses
Subscriptions, hardware lifecycles and firmware support dates. How to avoid running a security device that no longer receives updates.
Cybersecurity and Firewalls
Logs and SIEM for mid-size firms: what to collect and why
Firewall, identity, endpoint and email logs answer most investigations. How to start small and avoid drowning in data.
Cybersecurity and Firewalls
A startup security baseline for the first 90 days
Startups are targets because they hold code, data and cloud keys with few defences. Twelve steps that cover most real risk.
Cybersecurity and Firewalls
Protecting patient data: practical controls for clinics and hospitals
Encryption, role-based access, audit trails and secure links between laboratories and doctors. Aligning to HIPAA-style safeguards and India's DPDP Act.
Cybersecurity and Firewalls
Passwords, password managers and privileged access in a business
Shared admin passwords and spreadsheets are still common. Vaults, rotation and session recording make privileged access safer and auditable.
Questions
Frequently asked questions
By throughput needs, user and device count, VPN concurrency and the number of segments required — sized from your actual environment, not a generic recommendation.
Policy is tuned to your traffic, segments are defined, and reporting is set up — a firewall is a starting point for ongoing policy management, not a one-time appliance swap.
Yes, through VLAN segmentation and firewall policy that keeps each traffic class on its own trust zone.
Scope is defined per contract — from basic alerting to more active monitoring — and KINNEX will not describe a service as round-the-clock SOC coverage unless it is actually staffed and contracted that way.
Licence terms and renewal dates are tracked centrally and flagged ahead of expiry, so protection does not lapse silently.
Review your security architecture
Tell us the site, the constraint or the outcome you need, and we will come back with the right next step.